Latest tech news
Every story, newest first.
Vulnerability Watch, November 14, 2026: 8 critical CVEs and 81 new vendor and CERT advisories
Every critical-severity CVE NIST published in the past day, plus the latest advisories from national CERTs and vendors.
 NIST
Four New CNCF User Groups Give End Users Direct Access to Its TAB
The Cloud Native Computing Foundation created long-lived User Groups to address specific industry needs and guide projects across domains like platform engineering and public sector.
 CNCF
CVEs that matter, November 14, 2026: 3 to patch first, 3 exploited
This week's vulnerabilities with real evidence of attack, led by CVE-2026-123039 in Check Point Multiple Products.
CISA
Dropbox Plans $1.0 Billion Convertible Notes Offering Due 2031
Dropbox plans to raise $1.0 billion through convertible senior notes due 2031 to pay down debt and repurchase shares of its Class A common stock.
Company filings with the US SEC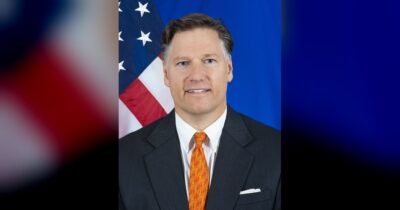
BreakingUS and Singapore Officials Discuss Digital and Tech Priorities
U.S. and Singapore officials met to advance shared digital priorities, including cybersecurity and secure technology supply chains.
US State Department
Europol Takedown Exposes 179,745 Accounts Linked to CastleRAT
Europol and international law enforcement dismantled CastleRAT malware infrastructure, adding 179,745 compromised accounts to Have I Been Pwned.
 Have I Been Pwned
BlackNevas Ransomware Destroyed Virtualization Estate Without ESXi Flaws
Kaspersky researchers found that BlackNevas ransomware destroyed an organization's virtualization estate over ten days using legitimate vCenter features.
 Kaspersky
Australia Plans Mandatory AI Safety and Security Protections
Australia plans mandatory AI safety and security protections for frontier AI companies, including a new regulator and penalties.
Prime Minister of Australia
The Privacy Week, November 13, 2026: How to Use Signal for Secure and Private Messaging
This week in privacy: 6 stories, led by How to Use Signal for Secure and Private Messaging.
 TechUpscale
Check Point Multiple Products flaw CVE-2026-123039 is being actively exploited, CISA warns
CISA added the Check Point Multiple Products vulnerability to its Known Exploited Vulnerabilities catalog on November 13, 2026, with a federal remediation deadline of November 16, 2026.
CISA